







SAP users are being advised by security firm Onapsis to review their software configuration settings to mitigate the risk of a default setting that could expose all SAP implementations to exploitation by attackers.
Onapsis released a report on April 26 detailing the configuration vulnerability that impacts SAP NetWeaver, which is a foundational component for running many SAP applications, including ERP and S/4 HANA. According to Onapsis, the default configuration for NetWeaver allows hackers to remotely attack a NetWeaver instance without authentication, gaining unrestricted access to all of the information on the system.
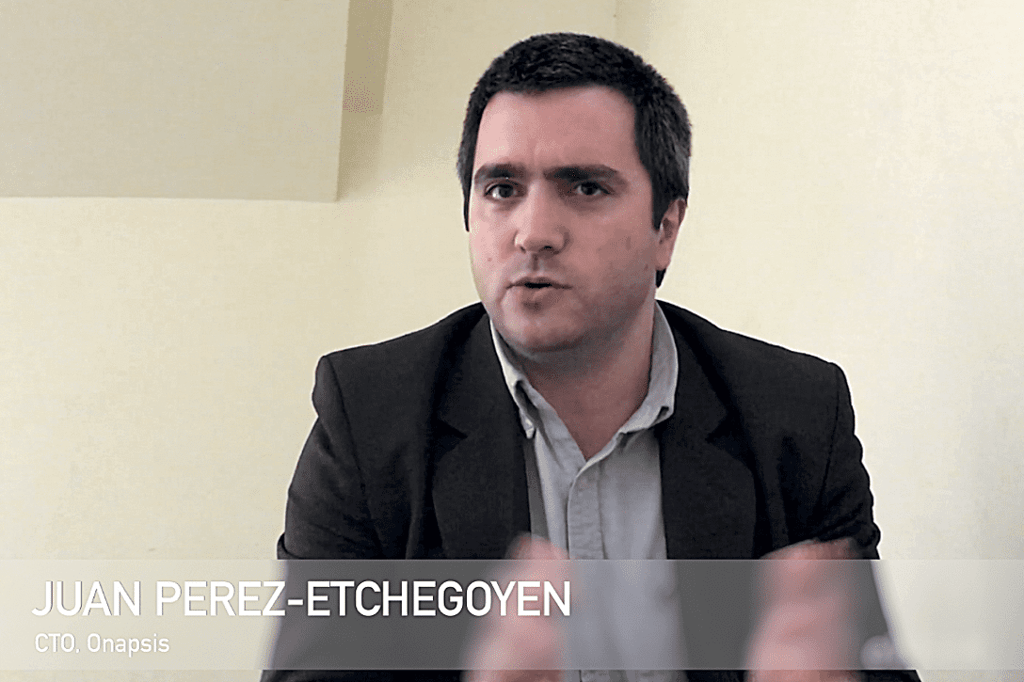
In a video interview with eWEEK, Juan Perez-Etchegoyen, CTO of Onapsis, discusses what the vulnerability is all about and why—despite his firm raising the alarm now—it’s not a new issue.
According to Perez-Etchegoyen, the configuration issues his firm discovered were actually identified by SAP in a series of security notes published in 2005. An SAP security note is a document that includes recommended best practices for configuration and deployment. The problem is that even though SAP documented the issue 13 years ago, it is not a default configuration and many organizations haven’t made the change.
In fact, according to Onapsis’ research conducted over the course of 2017, 90 percent of the SAP systems surveyed were at risk from the NetWeaver configuration flaw.
Perez-Etchegoyen said the configuration flaw is in the NetWeaver message server, which handles load balancing and communications between SAP application servers. With a connection to the misconfigured message server, an attacker can register a rogue application server and then execute a variety of attacks against SAP applications.
“From a configuration standpoint, it’s not so complex to fix as other vulnerabilities in SAP,” Perez-Etchegoyen said. “Typically, because of the complexity of SAP applications, sometimes it is really complex to close the security risk, but in this case the advantage is they can and should patch it quicker.”
SAP customers can get access to the security notes now, including 821875, 1408081 and 1421005, to make the necessary changes.
Watch the full video interview with Perez-Etchegoyen above.
Sean Michael Kerner is a senior editor at eWEEK and InternetNews.com. Follow him on Twitter @TechJournalist.