






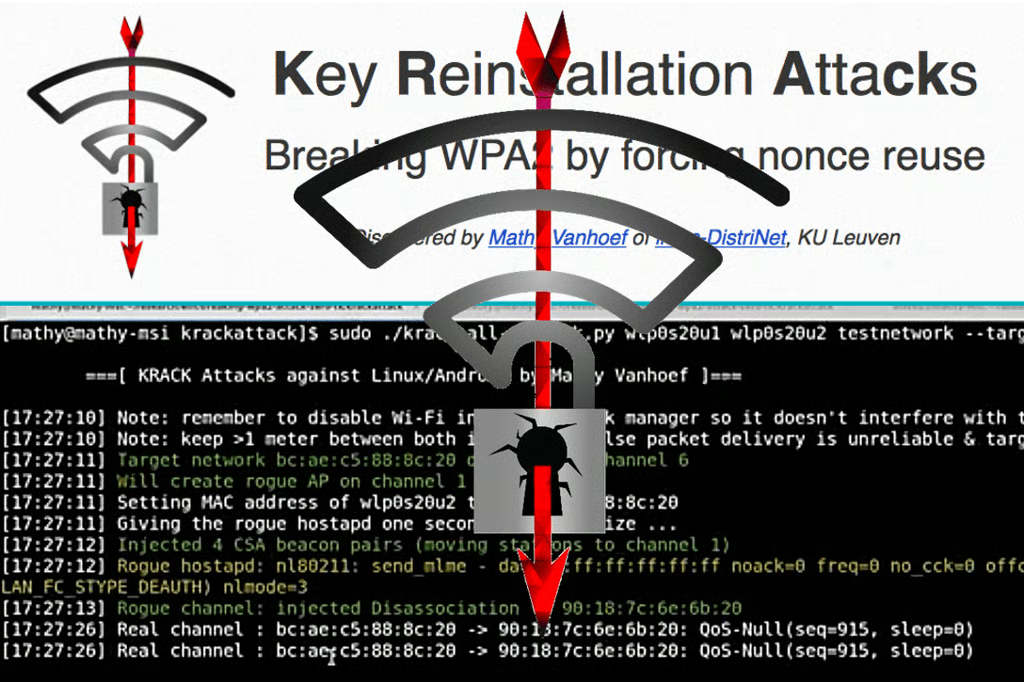

The WPA2 protocol that is widely used to secure WiFi traffic is at risk from multiple vulnerabilities, collectively referred to as “KRACK Attacks,” which were publicly disclosed on Oct. 16.
“Attackers can use this novel attack technique to read information that was previously assumed to be safely encrypted,” the vulnerability disclosure warns. “The attack works against all modern protected Wi-Fi networks.”
KRACK is an acronym for Key Reinstallation Attacks, which were discovered by security researchers Mathy Vanhoef and Frank Piessens working at Belgian University KU Leuven. The researchers have disclosed the details of the KRACK attack in a research paper and plan on discussing it further in talks at the Computer and Communications Security (CCS) and Black Hat Europe conferences later this year.
In total, the KRACK attacks include 10 vulnerabilities: CVE-2017-13077, CVE-2017-13078, CVE-2017-13079, CVE-2017-13080, CVE-2017-13081, CVE-2017-13082, CVE-2017-13084, CVE-2017-13086, CVE-2017-13087 and CVE-2017-13088. The different CVEs refer to variations of the key reinstallation attack that impact WPA2.
The KRACK vulnerabilities define new approaches to exploit the way that WPA2 generates a session encryption key. The researchers note that all WPA2-protected WiFi networks use the four-way handshake to generate a fresh session key.
“So far, this 14-year-old handshake has remained free from attacks, and is even proven secure,” the research abstract states. “However, we show that the 4-way handshake is vulnerable to a key reinstallation attack.”
The reinstallation attack is a form of replay attack, where an attacker tricks a victim into reinstalling an already-in-use key. KRACK attacks work by manipulating and replaying handshake messages, the researchers said. Of note, they said the KRACK attack methods do not actually reveal the password of a WPA2-protected WiFi network. In addition, the attacks do not recover any parts of a fresh encryption key that is negotiated during the four-way handshake.
Impact
The potential impact of the KRACK vulnerabilities is large and could well involve all users of WP2-protected WiFi.
“The weaknesses are in the Wi-Fi standard itself, and not in individual products or implementations,” Vanhoef wrote. “Therefore, any correct implementation of WPA2 is likely affected.”
At this point, Vanhoef said there is no indication that the KRACK vulnerabilities have been exploited in the wild by an attacker, though he cautions that it is possible.
“We are not in a position to determine if this vulnerability has been (or is being) actively exploited in the wild,” Vanhoef wrote. “That said, key reinstallations can actually occur spontaneously without an adversary being present! This may for example happen if the last message of a handshake is lost due to background noise, causing a retransmission of the previous message.”
According to Vanhoef, Android, Linux, Apple, Windows, OpenBSD, MediaTek, Linksys and many other vendors are affected by some variant of the KRACK attacks. Vanhoef worked with CERT/CC to conduct a coordinated private disclosure that was sent out to impacted vendors on Aug. 28. Multiple vendors have already issued patches to fix the issues, including Aruba, Cisco, Red Hat, Juniper Networks, ZyXEL, Samsung and Intel.
“Changing the password of your WiFi network does not prevent (or mitigate) the attack,” Vanhoef wrote. “Instead, you should make sure all your devices are updated, and you should also update the firmware of your router.”
Sean Michael Kerner is a senior editor at eWEEK and InternetNews.com. Follow him on Twitter @TechJournalist.