




How Notorious Trojans Hit Banks and Steal Your Money
Trojans for Sale
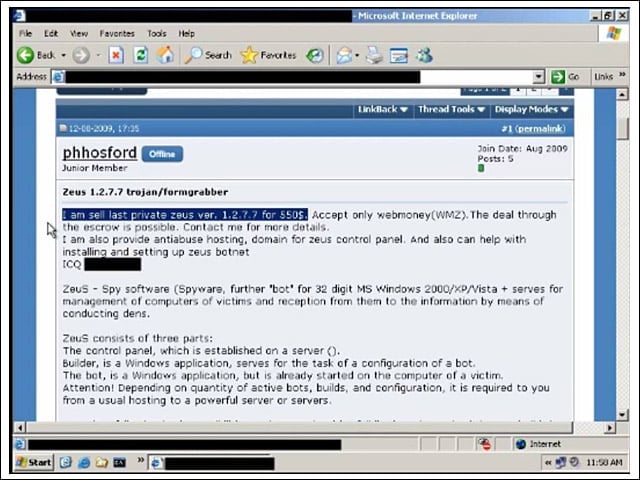
The Zeus crimeware toolkit has been around for years, and has been linked to a number of data theft operations, including the notorious “Rock Phish” group. The toolkit has become widely available in the cyber-underground. Here is an example of a “for sale” posting for the Trojan.
Infect Yourself? No Problem
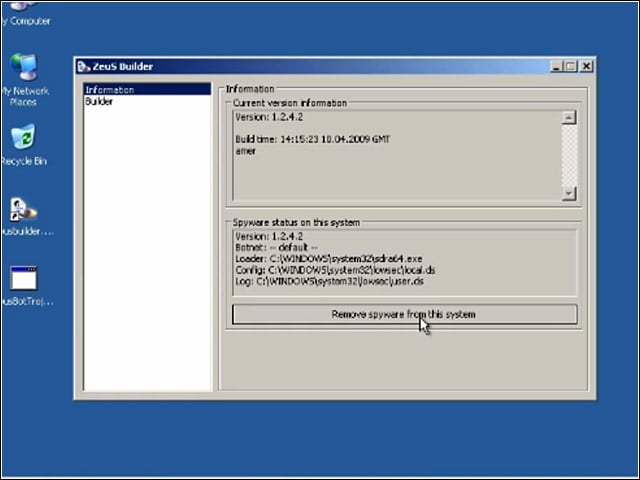
Some toolkits come with the ability to remove malware if would-be attackers accidentally infect themselves.
Master and Commander of the Cyber-Underground
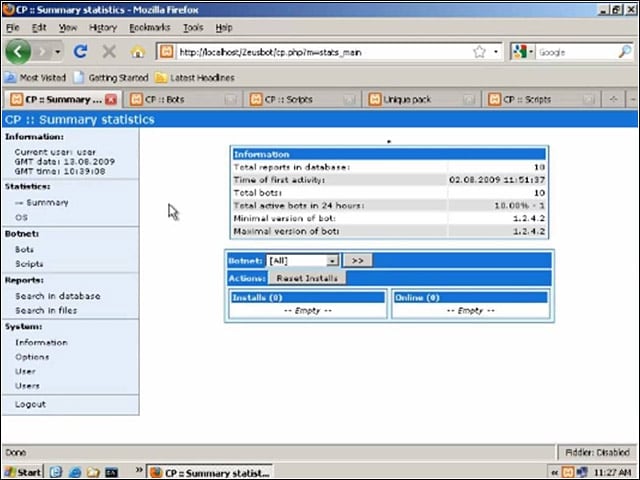
Many toolkits contain a command and control utility that is added to a Web server and used to manage the botnet.
Room for One More
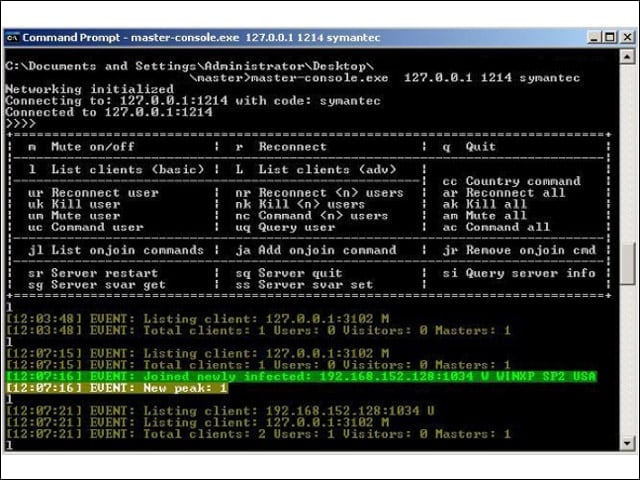
The subject of this slide is Trojan.Pilleuz, a worm that spreads through file-sharing programs, removable drives and Microsoft instant messaging clients. When executed, it connects to one or more of several network addresses and opens a backdoor on the compromised computer. The screenshot below shows the master console of the botnet after a newly infected system has joined. The worm is believed to stem from the Butterfly bot kit, which is no longer for sale.
Clampi Infection Rates
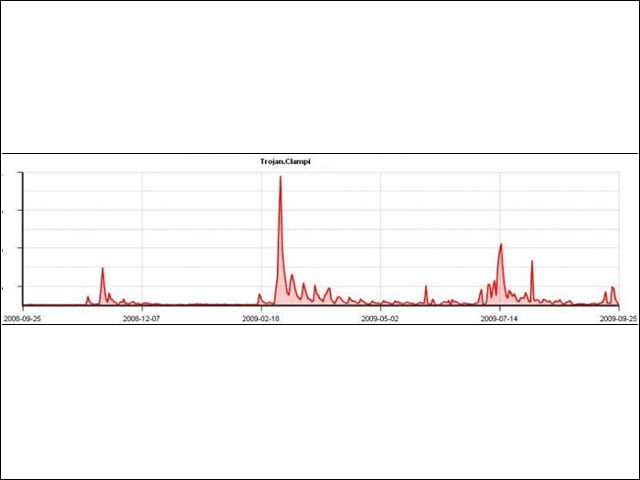
This graph depicts the spread of the Clampi Trojan over the past year as observed by Symantec. There are two notable spikes that correspond to the release of updates to this Trojan. The variant released on July 15, 2009, is what Symantec is currently seeing in the wild.
Stealing the Data
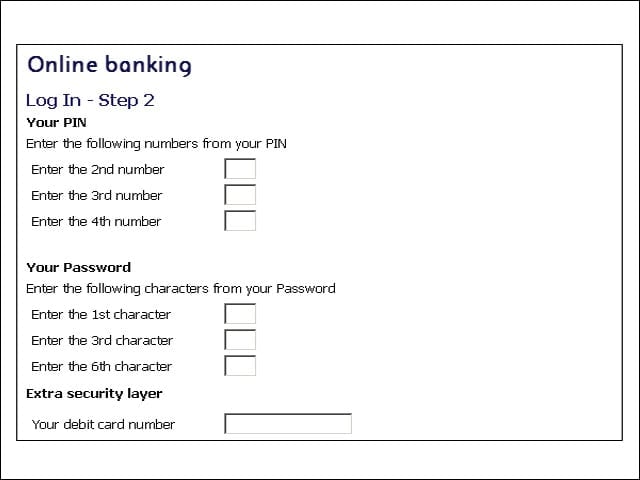
This from a Clampi infection. Here, the Trojan is injecting a fake form into a banking log-in session. The idea is for the user to see this page in her browser and think it is legitimate—unfortunately for the user, it is not.
Stealing the Data, Reloaded
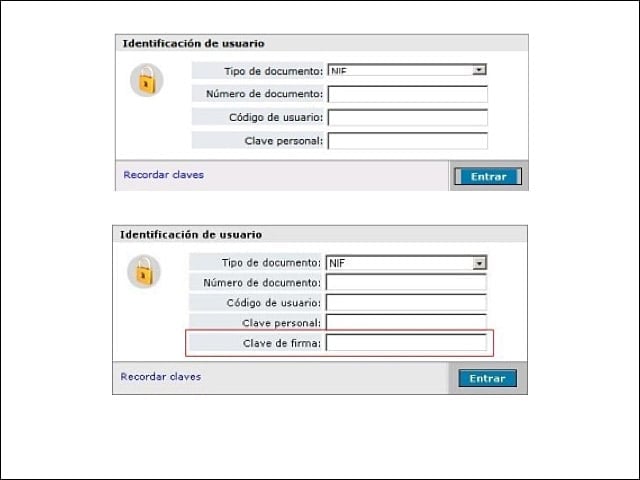
This is a side-by-side comparison of log-in forms. You’ll notice slight differences between the two. The fake one has an extra field, courtesy of Trojan.Silentbanker. Silentbanker records keystrokes, captures screen images and steals confidential financial information to send to a remote attacker.
Malicious Links Leading to Malware
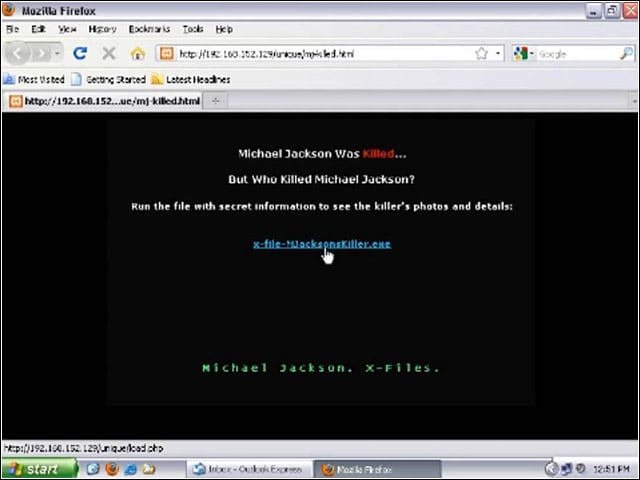
We end at the place where it all starts for phishing victims—the infection. In the example here, the user is tricked into visiting a malicious site. This one promises the visitor information about the “murder” of pop star Michael Jackson. All users have to do to get infected is click on the link on the page.
Money Mules Transfer Profits
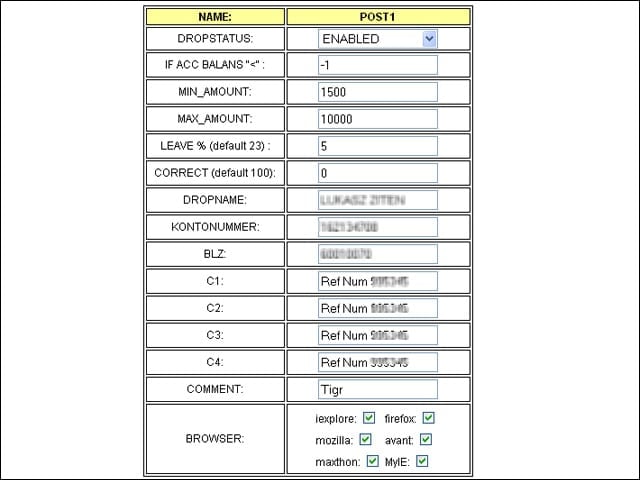
In the case of the URLZone Trojan, the gang behind it uses money mules to get the money from the stolen accounts. Here is a money mule definition screen that includes the maximum and minimum amount to steal, the money mule account details, enable/disable flags and the comments for the fraud transaction (money transfers often include comments such as the reason for transferring the money, Finjan researchers explained).