






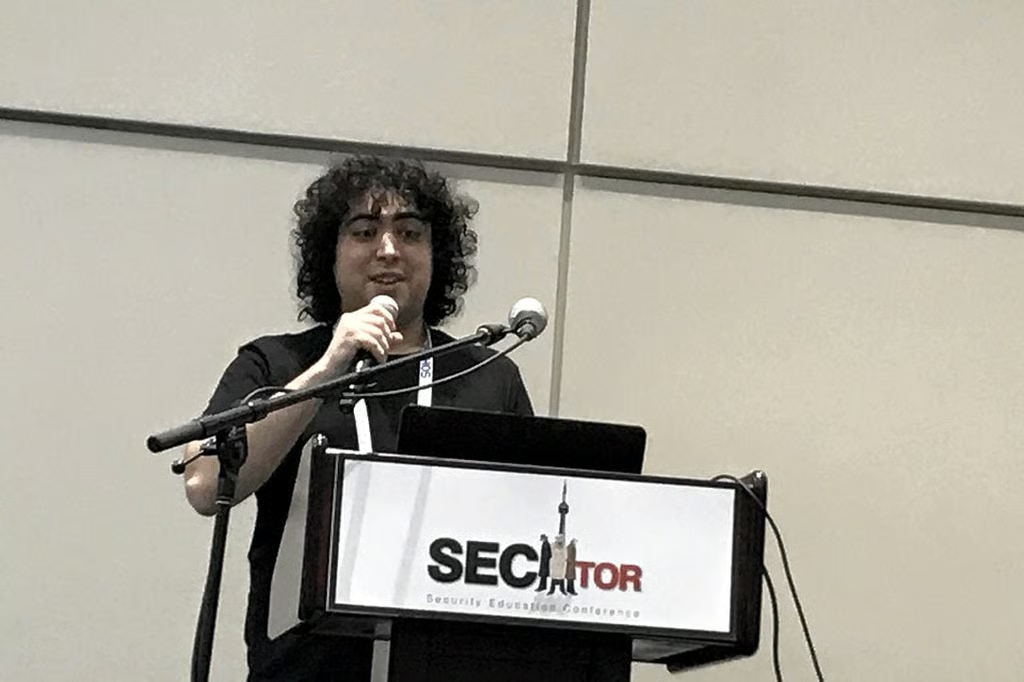

TORONTO—There are a lot of ways to hack a A security researcher explains how WPA2 Enterprise wireless security can be bypassed and why the EAP-TLS wireless authentication protocol should be more widely deployed to help mitigate risks. WiFi network, and Gabriel Ryan, security engineer at security firm Gotham Digital Science, detailed many of them in a session at the SecTor conference here on Nov. 14.
During his session, titled “The Black Art of Wireless Post-Exploitation,” Ryan demonstrated the new EAPhammer tool that he created to hack WPA2-Enterprise networks. He also detailed new attack methods to bypass misconfigured WPA2 WiFi networks, including a wireless pivot attack. While there is no shortage of attack methods, Ryan also strongly advocated for the use of the EAP-TLS (Extensible Authentication Protocol Transport Layer Security) protocol to help stop multiple forms of WiFi attack.
Ryan explained that while WPA2 WiFi protection encrypts data sent wirelessly, an area of weakness where potential attacks can be performed is during the initial “handshake” connection, when the wireless user starts a connection.
The EAPhammer toolkit that Ryan developed and demonstrated during his SecTor session can help security researchers perform what is known as an “evil twin” attack against WPA2-Enterprise networks. In an evil twin attack, a rogue access point is set up to mimic the address and connectivity of an authentic WiFi access point.
“It [EAPhammer] is designed to be used in full scope wireless assessments and red team engagements,” the GitHub project page states. “As such, focus is placed on providing an easy-to-use interface that can be leveraged to execute powerful wireless attacks with minimal manual configuration.”
Among the new attacks that EAPhammer can help execute is one that Ryan calls an indirect wireless pivot using a hostile portal attack. In that attack scenario, a WiFi access point that has a captive portal is attacked, with the hacker gaining access to the back-end restricted virtual LAN (VLAN). Captive portals are commonly used in hotels among other places, requiring users to log into a page first to provide payment information and gain access.
Ryan also detailed how it is possible to outmaneuver wireless client isolation to attack other devices on a WiFi network. Wireless client isolation is a commonly deployed best practice to help protect public networks, where administrators don’t want end users to be able to connect to a restricted VLAN or to other users on the same WiFi access point.
“The problem with WiFi client isolation is that it’s a logical control and not a physical control,” he said.
Among the tools that can help security researchers bypass WiFi client isolation is WiFitap. Also, the Aircrack suite of tools now has client isolation bypass capabilities, Ryan said.
EAP-TLS
While WPA2 can be attacked by multiple mechanisms, Ryan noted that the EAP-TLS authentication framework for WiFi provides protection against the attacks he described.
EAP-TLS requires security certificates on both sides of the wireless connection, providing a more resilient approach to connecting to a WiFi access point. Ryan said that using EAP-TLS effectively eliminates the ability of attackers to execute a rogue access point attack. The challenge, he added, is that EAP-TLS has long been difficult to implement in an enterprise network.
Ryan noted that security versus convenience is an issue with EAP-TLS, with the ease-of-use limiting usage, even though it is more secure than other WiFi authentication protocols.
“There is no magic bullet here, and security with convenience is often a paradox,” he said. “The current trend is now to focus more on breach containment than breach prevention.”
In the final analysis, Ryan noted that implementing EAP-TLS in 2017 is not as difficult as it once was. He suggested that organizations use mobile device management (MDM) technologies to help deploy and use EAP-TLS as part of a new device on-boarding process.
“As a community, we should question whether it is truly a sound business decision to neglect EAP-TLS in favor of a more reactive approach that focuses on access control and threat containment,” Ryan said.
Sean Michael Kerner is a senior editor at eWEEK and InternetNews.com. Follow him on Twitter @TechJournalist.